

The MS-102 PDF Dumps Greatest for the Microsoft Exam Study Guide!
Read Online MS-102 Test Practice Test Questions Exam Dumps
NEW QUESTION # 98
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.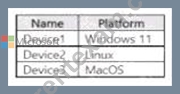
You plan to create an Endpoint security policy by using the Defender Update controls template. To which device can you apply the policy?
- A. Devke1, Device2. and Devke3
- B. Devke1 and Device3 only
- C. Device1 only
- D. Device1 and Devke2 only
Answer: C
NEW QUESTION # 99
You have a Microsoft 365 tenant that contains two users named User1 and User2. You create the alert policy shown in the following exhibit.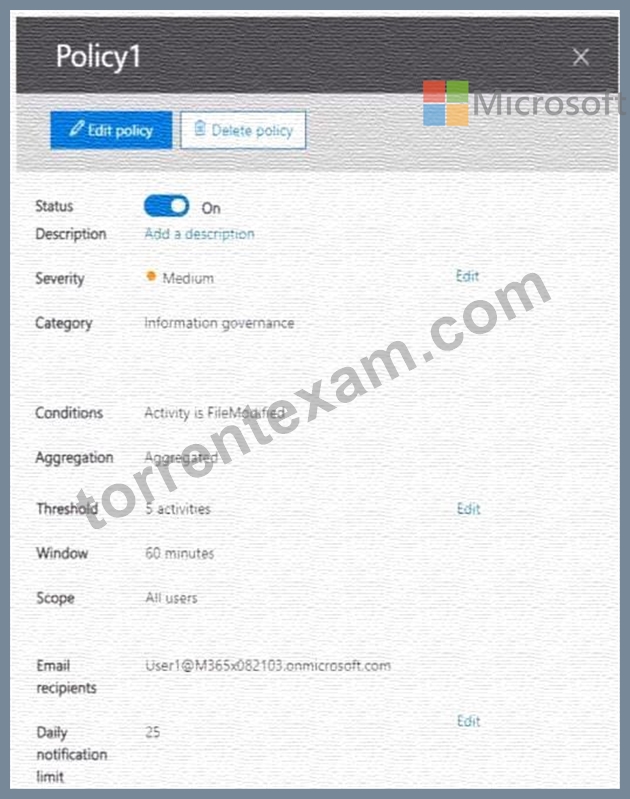
User2 runs a script that modifies a file in a Microsoft SharePoint Online library once every four minutes and runs for a period of two hours.
How many alerts will User1 receive?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
NEW QUESTION # 100
You have a Microsoft 365 E5 tenant
You create a data toss prevention (DLP) policy to prevent users from using Microsoft Teams to share internal documents with external users.
To which two locations should you apply the policy? To answer, select the appropriate locations in the answer area.
NOTE: Each correct selection is worth one point.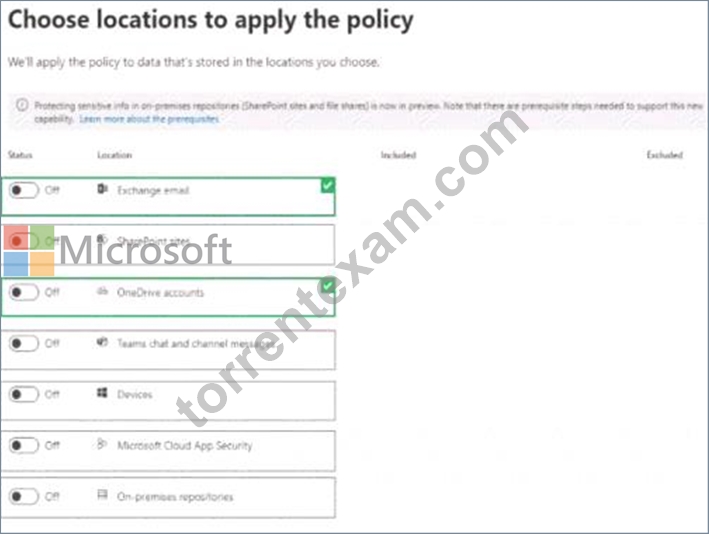
Answer:
Explanation: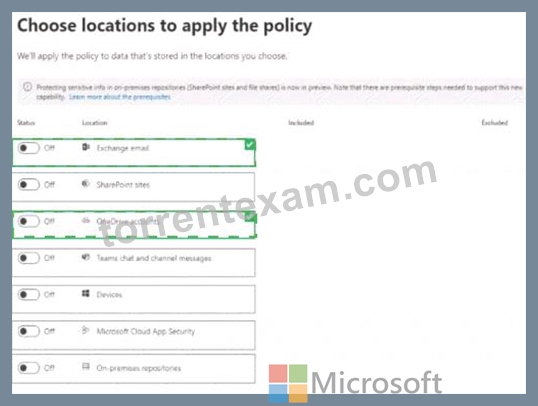
NEW QUESTION # 101
You have a Microsoft 365 E5 tenant that contains 100 Windows 10 devices.
You plan to attack surface reduction (ASR) rules for the Windows 10 devices.
You configure the ASR rules in audit mode and collect audit data in a Log Analytics workspace.
You need to find the ASR rules that match the activities on the devices.
How should you complete the Kusto query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.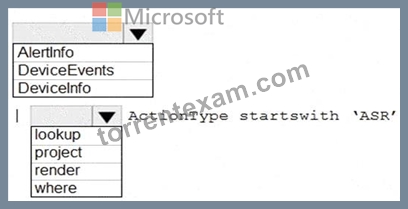
Answer:
Explanation: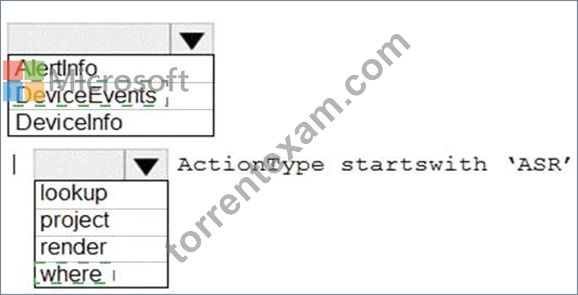
Explanation: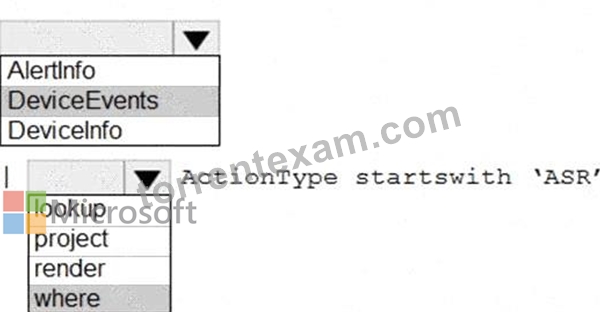
Reference:
https://techcommunity.microsoft.com/t5/microsoft-defender-for-endpoint/demystifying-attack-surface- reduction-rules-part-3/ba-p/1360968
NEW QUESTION # 102
You have a Microsoft 365 E5 subscription.
You need to configure Microsoft Defender for Office 365 to meet the following requirements:
* A user's email sending patterns must be used to minimize false positives for spoof protection.
* Documents uploaded to Microsoft Teams, SharePoint Online, and OneDrive must be protected by using Defender for Office 365.
What should you configure for each requirement? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.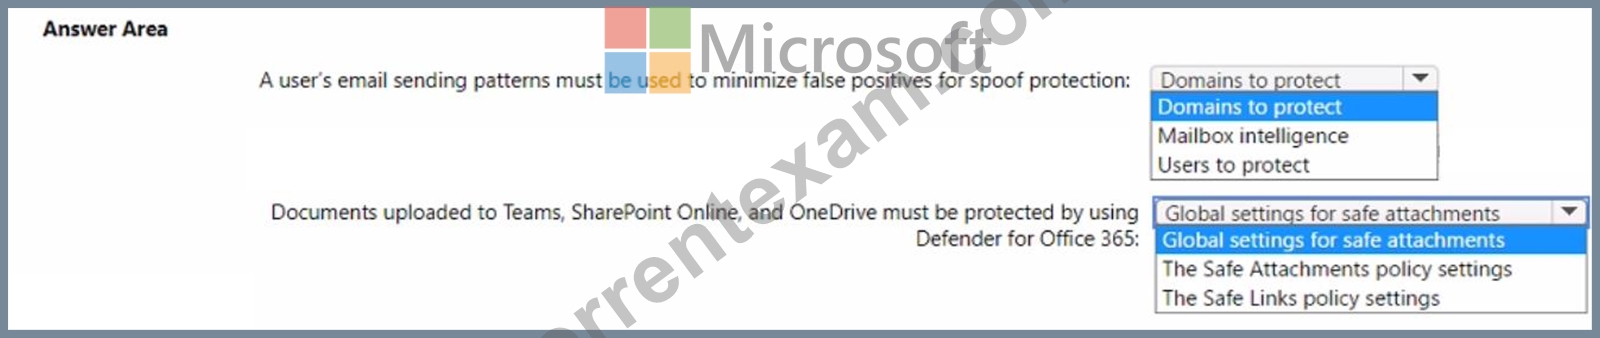
Answer:
Explanation: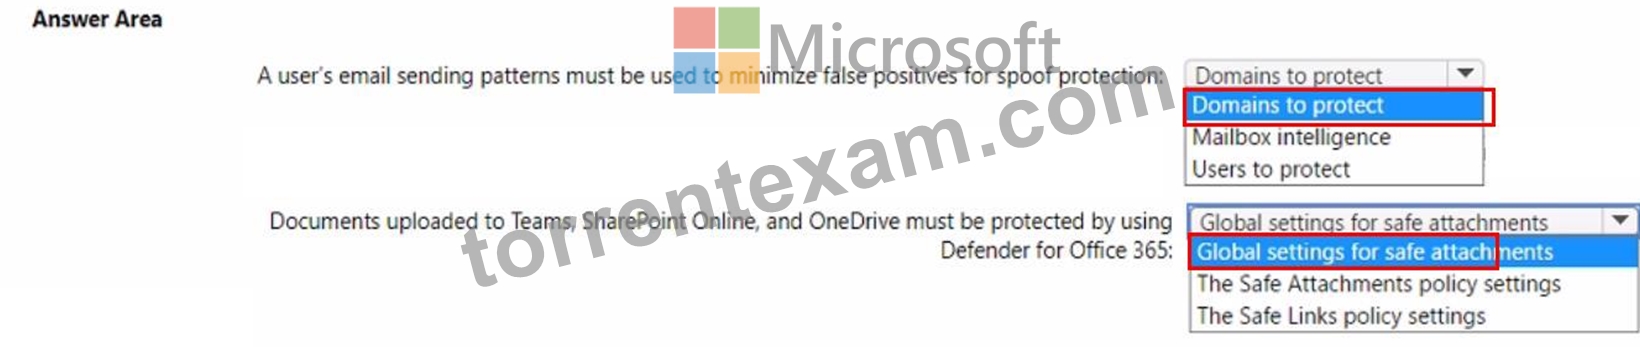
NEW QUESTION # 103
You have a Microsoft 365 E5 subscription that contains the security groups shown in the following table.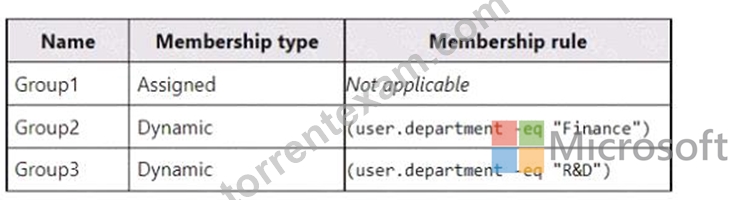
The subscription contains the users shown in the following table.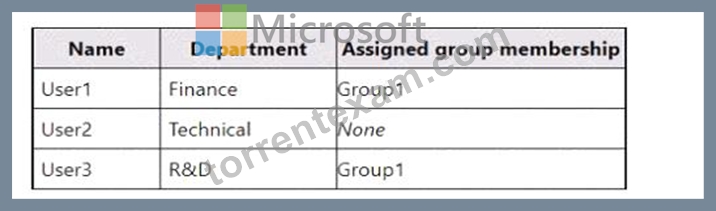
You have a Conditional Access policy that has the following settings:
* Assignments
o Users
Include: Group1
Exclude: Group2. Group3
o Target resources
Cloud apps
App1
Access controls
Grant
Block access
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.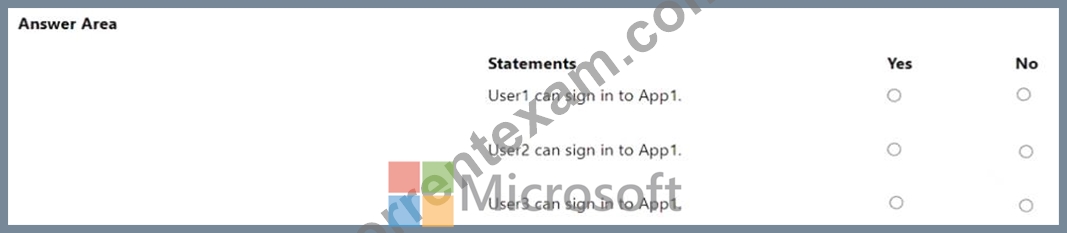
Answer:
Explanation:
Explanation: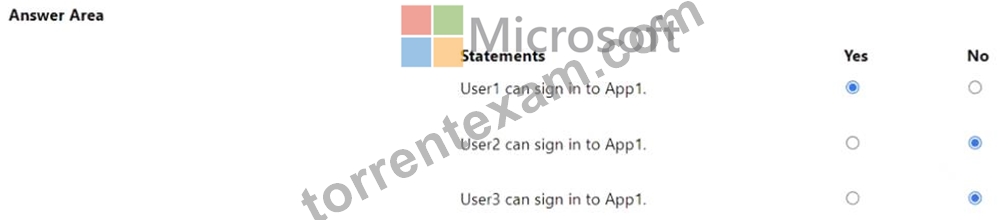
NEW QUESTION # 104 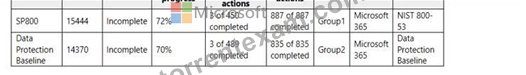
The SP800 assessment has the improvement actions shown in the following table.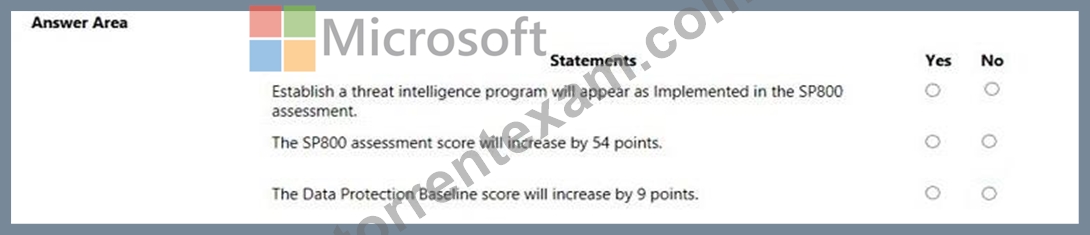
Answer:
Explanation: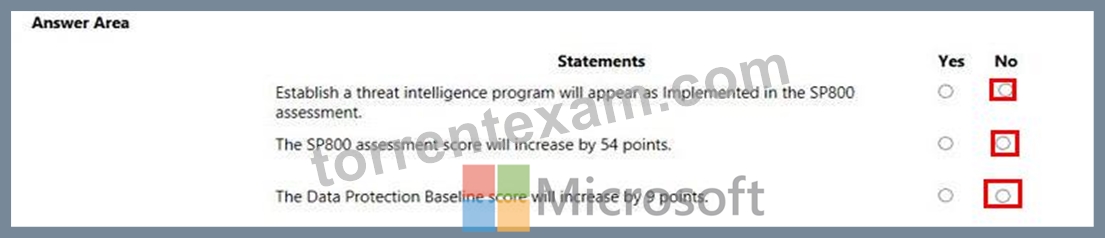
NEW QUESTION # 105
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.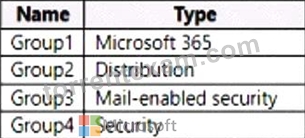
You plan to publish a sensitivity label named Label1.
To which groups can you publish Label1?
- A. Group1 and Group2 only
- B. Group1 and Group4 only
- C. Group1 only
- D. Group1 Group2, Group3, and Group4
- E. Group1, Group2, and Group3 only
Answer: C
Explanation:
In addition to using sensitivity labels to protect documents and emails, you can also use sensitivity labels to protect content in the following containers: Microsoft Teams sites, Microsoft 365 groups (formerly Office 365 groups), and SharePoint sites.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites
NEW QUESTION # 106
You have an Azure AD tenant that contains the administrative units shown in the following table.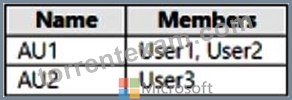
You have the following users:
A user named User1 that is assigned the Password Administrator for AU1 and AU2.
A user named User2 that is assigned the User Administrator for AU1.
A user named User3 that is assigned the User Administrator for the tenant.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.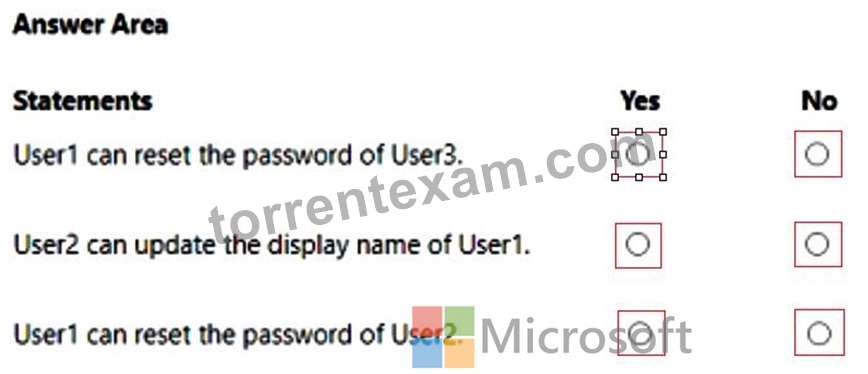
Answer:
Explanation: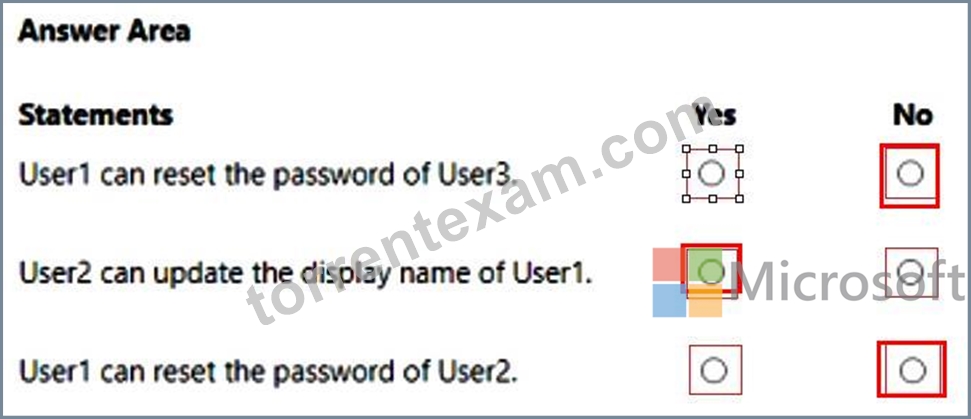
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/roles/permissions-reference#who-can-reset-passwords
https://learn.microsoft.com/en-us/azure/active-directory/roles/permissions-reference
NEW QUESTION # 107
You have device compliance policies shown in the following table.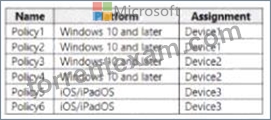
The device compliance state for each policy is shown in the following table.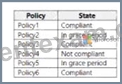
NOTE: Each correct selection is worth one point.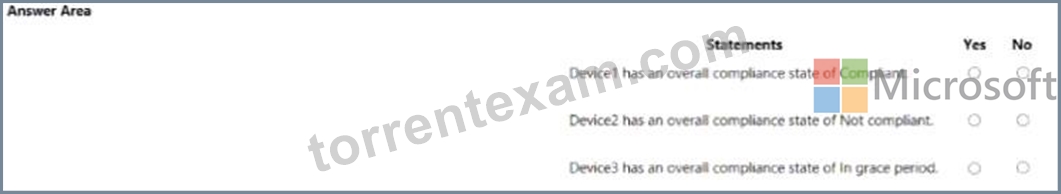
Answer:
Explanation:
Explanation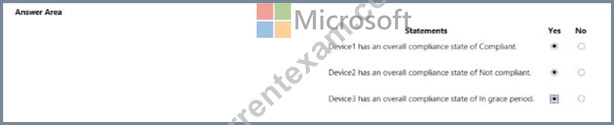
NEW QUESTION # 108
You have a Microsoft 365 subscription.
From the Microsoft 365 admin center, you open the Microsoft 365 Apps usage report as shown in the following exhibit.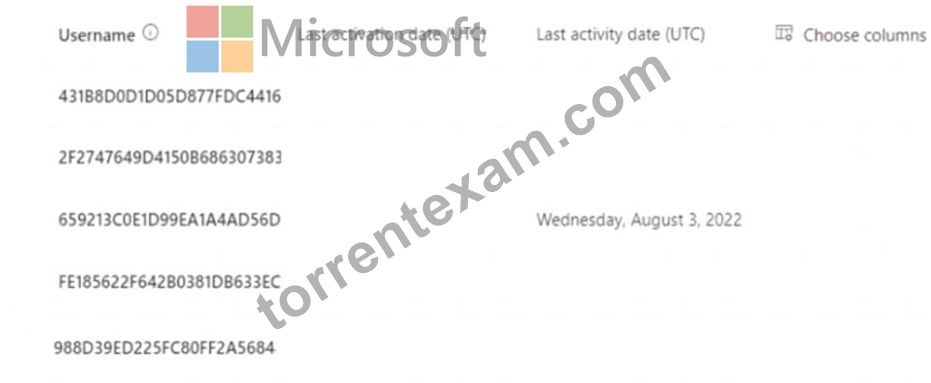
You need ensure that the report meets the following requirements:
* The Username column must display the actual name of each user.
* Usage of the Microsoft Teams mobile app must be displayed.
What should you modify for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.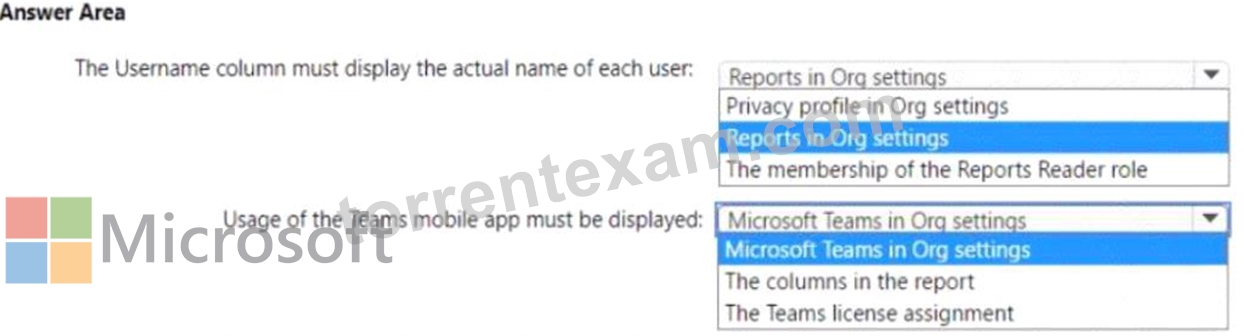
Answer:
Explanation: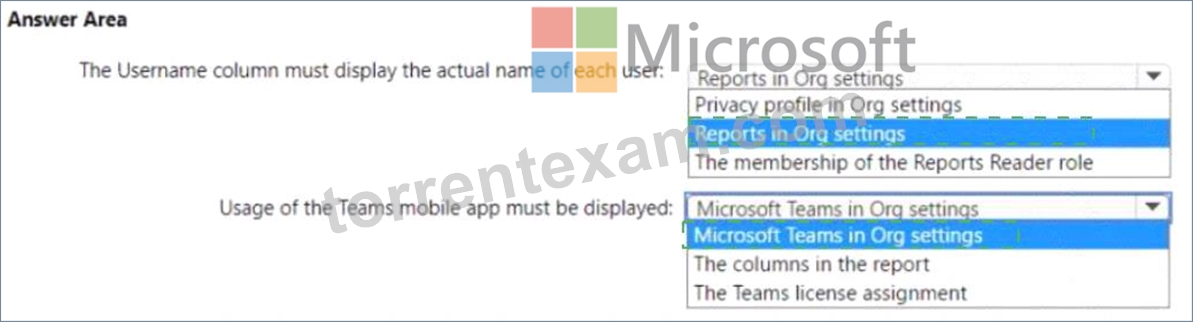
Explanation: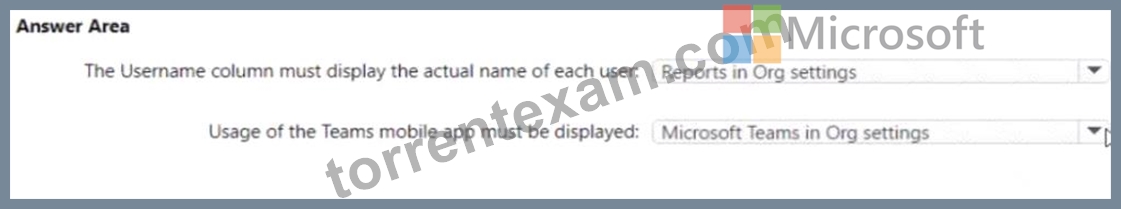
NEW QUESTION # 109
You have a Microsoft 365 E5 subscription that contains the resources shown in the following table.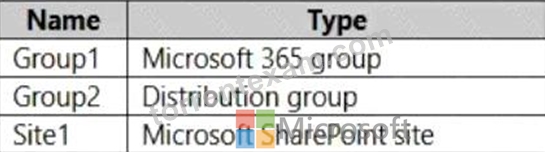
You create a sensitivity label named Label1.
To which resource can you apply Label1?
- A. Groupl and Group2 only
- B. Group1 only
- C. Group1, Group2, and Sitel
- D. Sitel only
- E. Group2 only
Answer: C
Explanation:
Explanation
Assign sensitivity labels to Microsoft 365 groups in Azure Active Directory Azure Active Directory (Azure AD), part of Microsoft Entra, supports applying sensitivity labels published by the Microsoft Purview compliance portal to Microsoft 365 groups.
In addition to using sensitivity labels to protect documents and emails, you can also use sensitivity labels to protect content in the following containers: Microsoft Teams sites, Microsoft 365 groups (formerly Office 365 groups), and SharePoint sites.
When you configure a label policy, you can:
Choose which users and groups see the labels. Labels can be published to any specific user or email-enabled security group, distribution group, or Microsoft 365 group (which can have dynamic membership) in Azure AD.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION # 110
You have a Microsoft 365 E5 subscription.
You need to create a Conditional Access policy that will require the use of FID02 security keys only when users join their Windows devices to Microsoft Entra ID.
How should you configure the policy? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.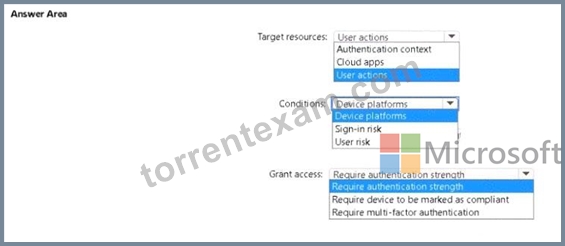
Answer:
Explanation: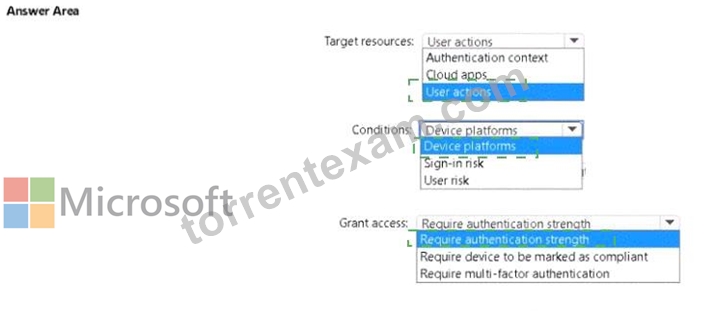
Explanation: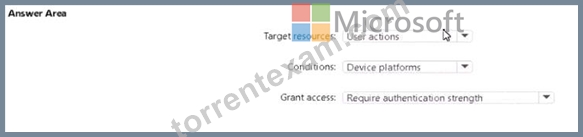
NEW QUESTION # 111
You have a Microsoft 365 E5 subscription.
You need to configure Privileged Identity Management (PIM) for the User Administrator role in Microsoft Entr a. Eligible users must meet the following requirements:
* Always be able to request the User Administrator role.
* Must provide a reason when requesting the User Administrator role
* Must require multi-factor authentication (MFA} when activating the User Administrator role The solution must minimize administrative effort.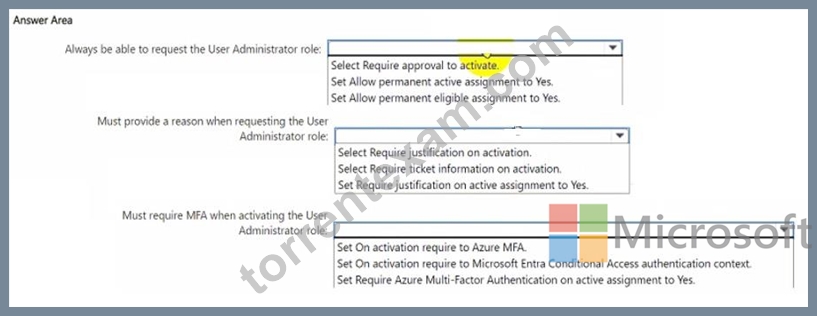
Answer:
Explanation: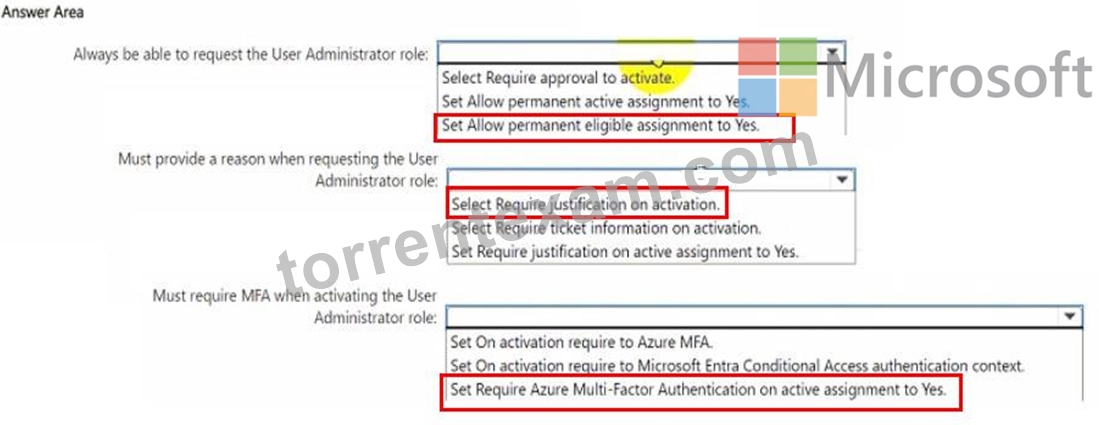
NEW QUESTION # 112
You have a Microsoft 365 E5 subscription.
You need to meet the following requirements:
Automatically encrypt documents stored in Microsoft OneDrive and SharePoint.
Enable co-authoring for Microsoft Office documents encrypted by using a sensitivity label.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.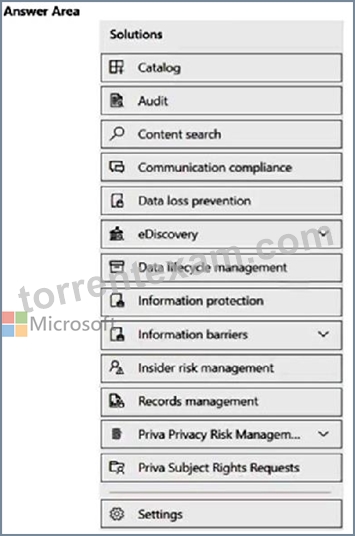
Answer:
Explanation: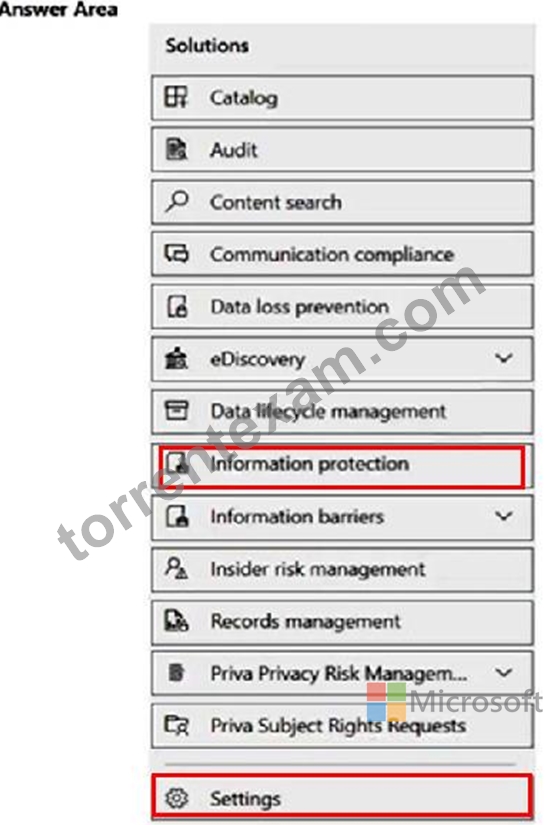
Reference:
https://learn.microsoft.com/en-us/defender-cloud-apps/azip-integration
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-coauthoring
NEW QUESTION # 113
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.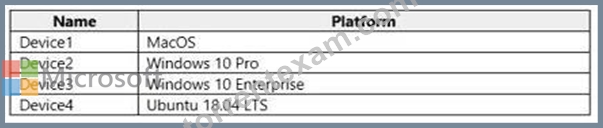
You plan to implement attack surface reduction (ASR) rules. Which devices will support the ASR rules?
- A. Device3 only
- B. Device1, Device2, Devices and Device4
- C. Device 1, Device2, and Device3 only
- D. Device2 and Device3 only
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/enable-attack-surface-reduction?
view=o365-worldwide#requirements
NEW QUESTION # 114
You configure an anti-phishing policy as shown in the following exhibit.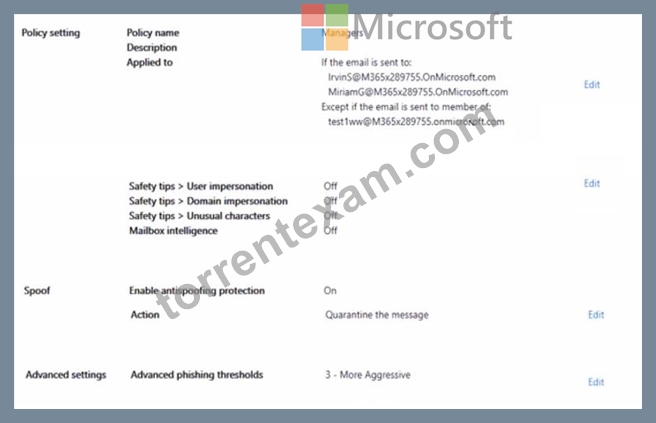
Use the drop-down menus to select the answer choke that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.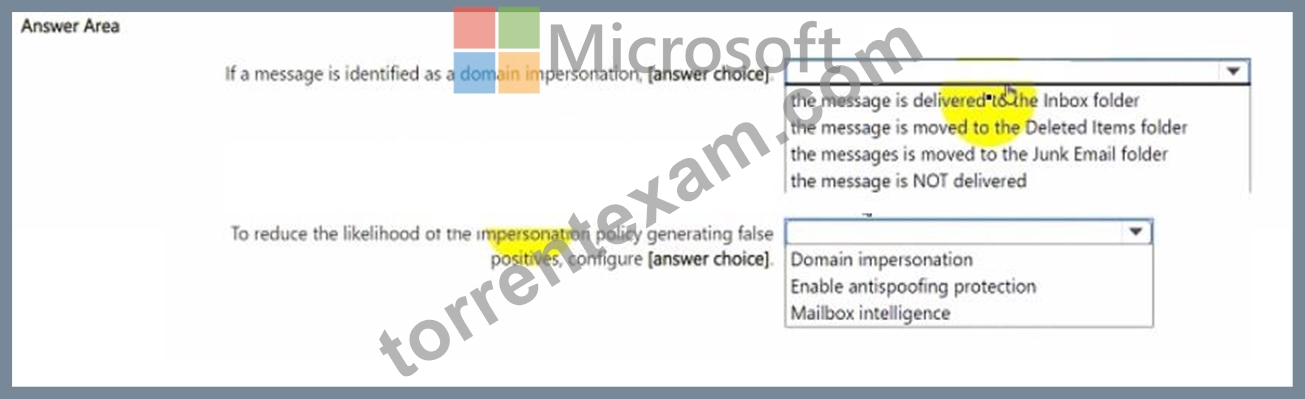
Answer:
Explanation: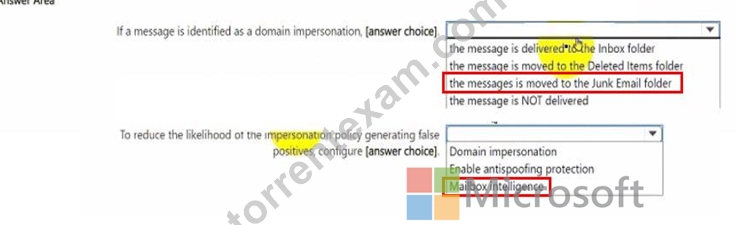
NEW QUESTION # 115
You have a Microsoft 365 tenant that contains the compliance policies shown in the following table.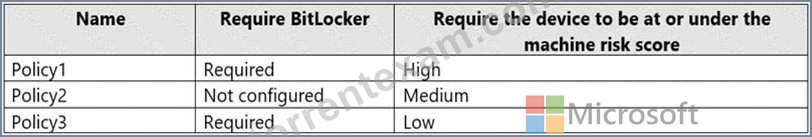
The tenant contains the devices shown in the following table.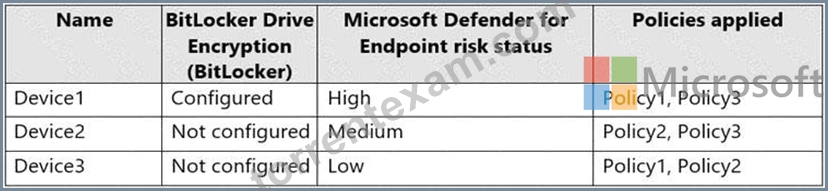
For each of the following statements, select Yes if the statement is true. Otherwise, select No.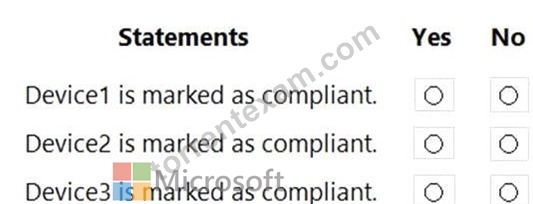
Answer:
Explanation: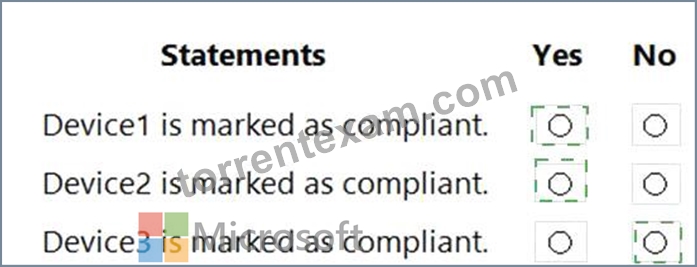
Explanation
Graphical user interface, text, application Description automatically generated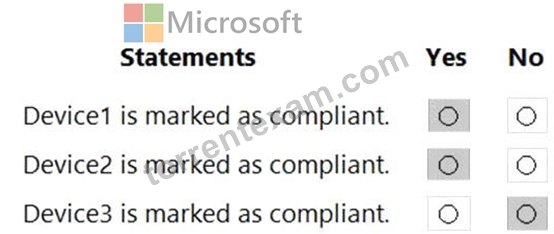
NEW QUESTION # 116
Your on-premises network contains an Active Directory domain.
You have a Microsoft 365 subscription.
You need to sync the domain with the subscription. The solution must meet the following requirements:
On-premises Active Directory password complexity policies must be enforced.
Users must be able to use self-service password reset (SSPR) in Azure AD.
What should you use?
- A. Azure AD Seamless Single Sign-On (Azure AD Seamless SSO)
- B. pass-through authentication
- C. Azure AD Identity Protection
- D. password hash synchronization
Answer: B
Explanation:
Explanation
Azure Active Directory (Azure AD) Pass-through Authentication allows your users to sign in to both on-premises and cloud-based applications using the same passwords.
This feature is an alternative to Azure AD Password Hash Synchronization, which provides the same benefit of cloud authentication to organizations. However, certain organizations wanting to enforce their on-premises Active Directory security and password policies, can choose to use Pass-through Authentication instead.
Note: Azure Active Directory (Azure AD) self-service password reset (SSPR) lets users reset their passwords in the cloud, but most companies also have an on-premises Active Directory Domain Services (AD DS) environment for users. Password writeback allows password changes in the cloud to be written back to an on-premises directory in real time by using either Azure AD Connect or Azure AD Connect cloud sync. When users change or reset their passwords using SSPR in the cloud, the updated passwords also written back to the on-premises AD DS environment.
Password writeback is supported in environments that use the following hybrid identity models:
Password hash synchronization
Pass-through authentication
Active Directory Federation Services
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-pta
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-sspr-writeback
NEW QUESTION # 117
You are evaluating the use of multi-factor authentication (MFA).
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.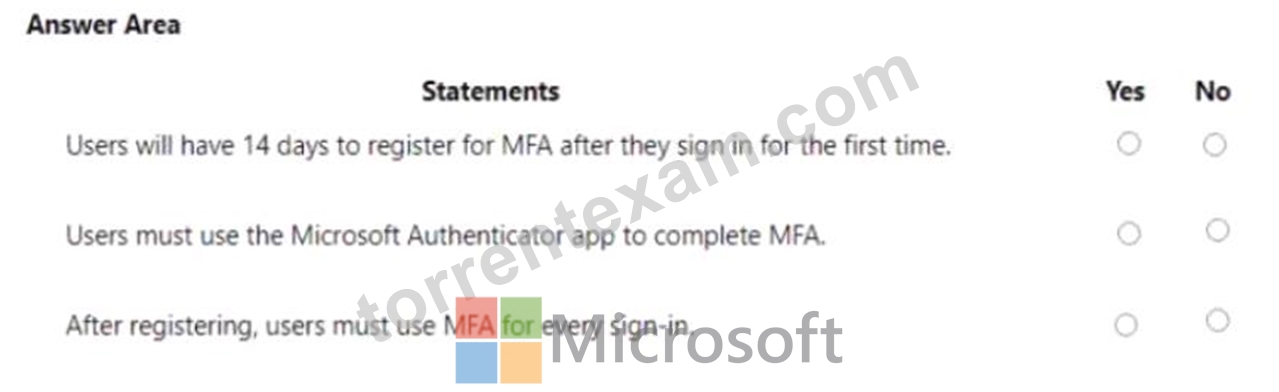
Answer:
Explanation: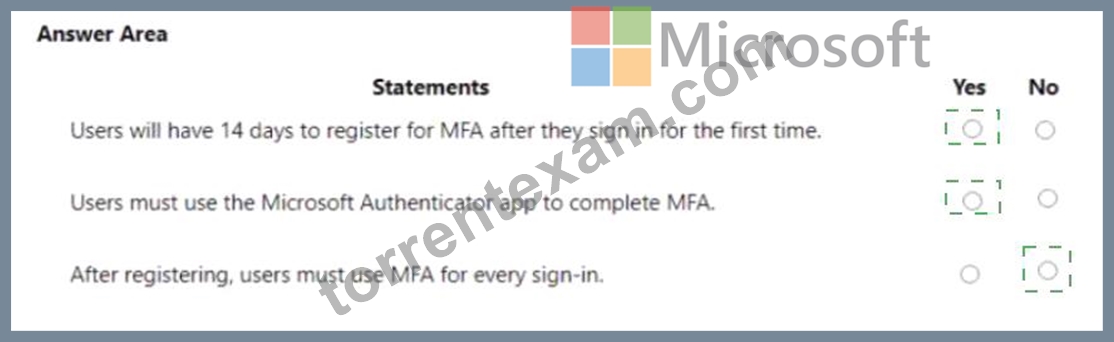
Explanation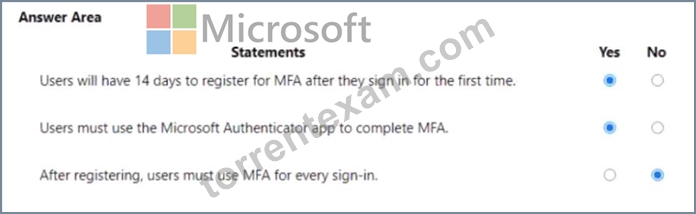
NEW QUESTION # 118
You have a Microsoft 365 E5 tenant.
The Microsoft Secure Score for the tenant is shown in the following exhibit.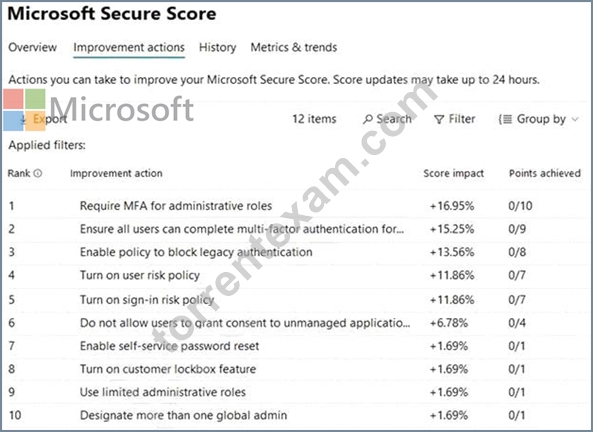
You plan to enable Security defaults for Azure Active Directory (Azure AD).
Which three improvement actions will this affect?
- A. Enable self-service password reset
- B. Ensure all users can complete multi-factor authentication for secure access
- C. Use limited administrative roles
- D. Require MFA for administrative roles.
- E. Enable policy to block legacy authentication
Answer: B,D,E
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/concept-fundamentals-security-defaults
NEW QUESTION # 119
HOTSPOT
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.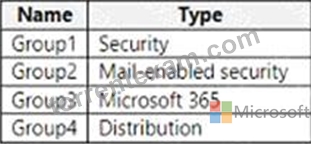
All the groups are deleted.
Which groups can be restored, and what is the retention period? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.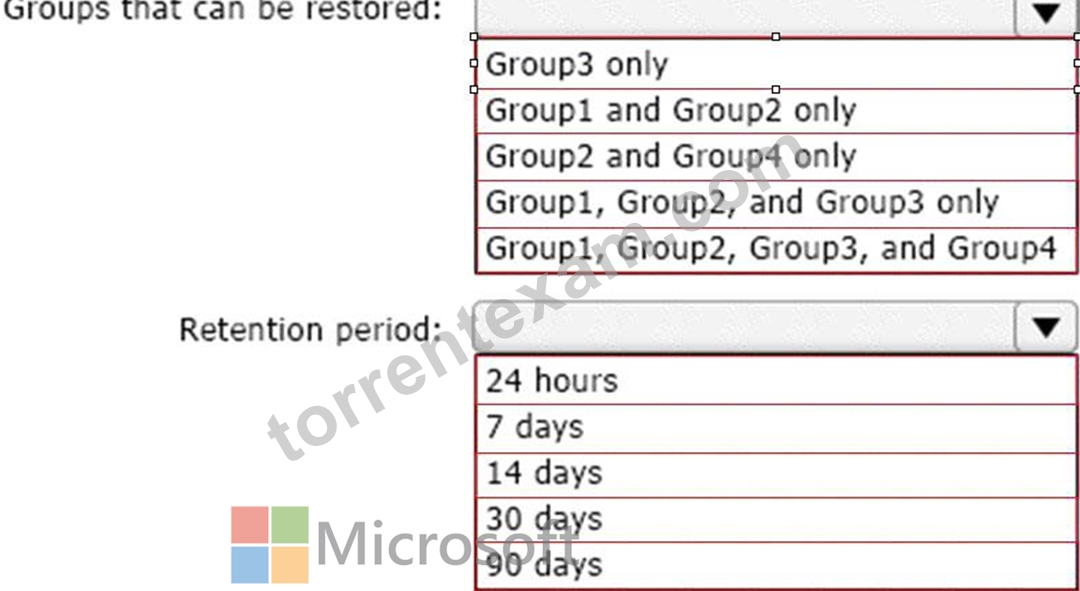
Answer:
Explanation: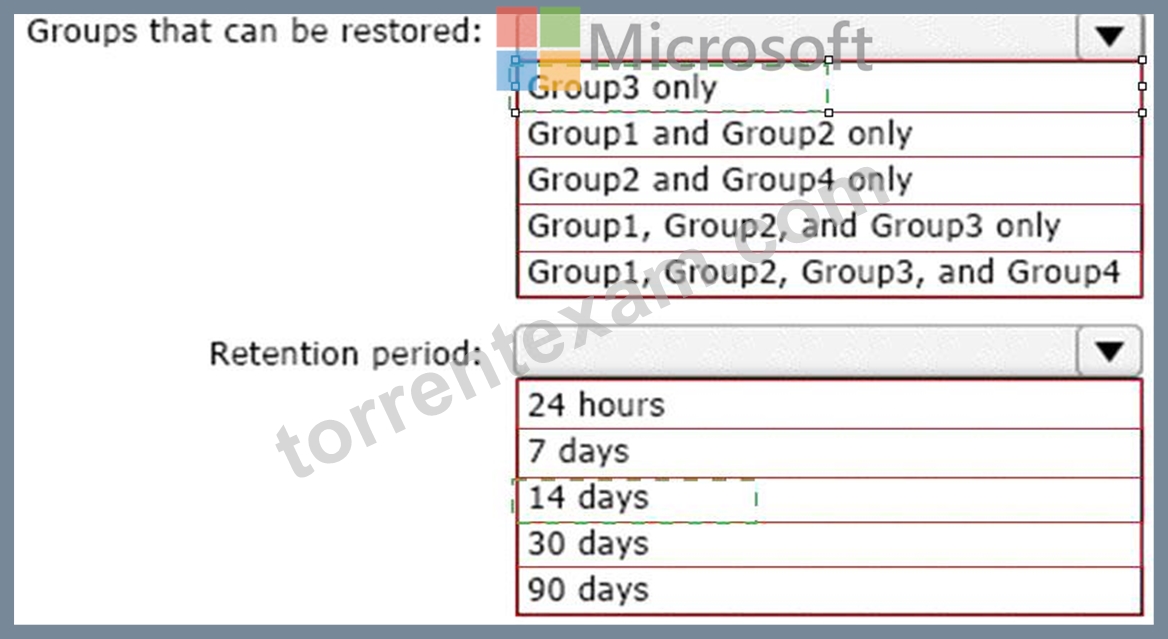
Explanation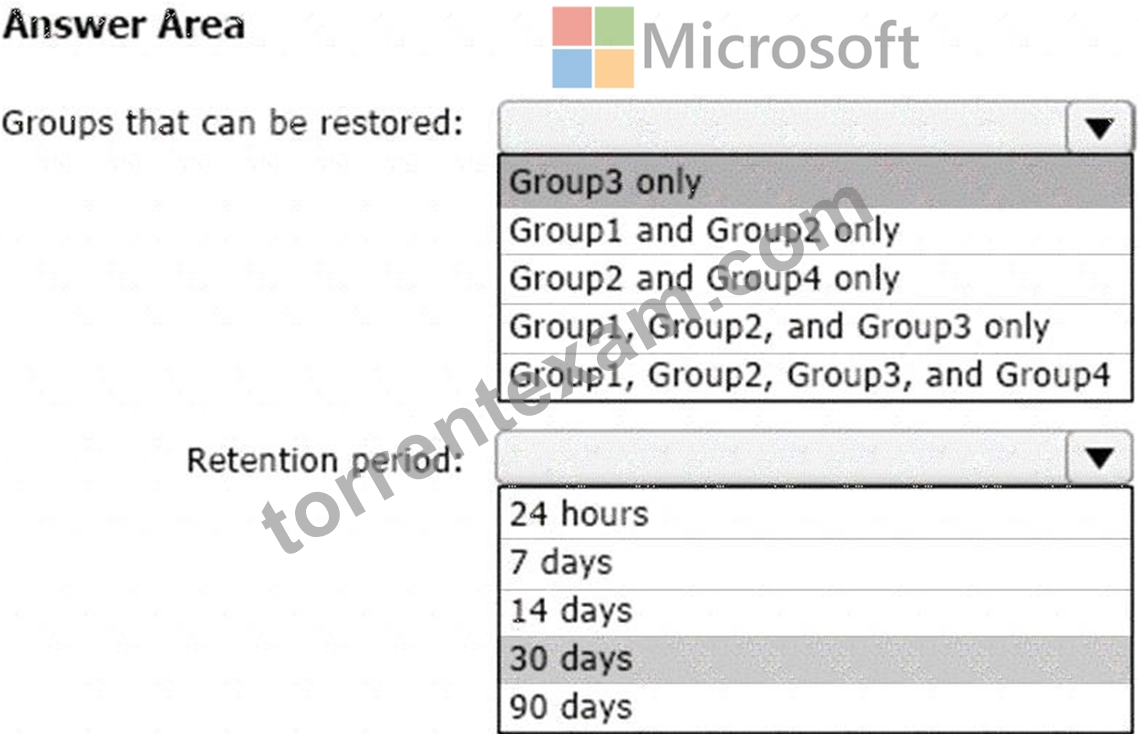
Box 1: Group3 only
Box 2: 30 days
If you've deleted a group, it will be retained for 30 days by default. This 30-day period is considered a
"soft-delete" because you can still restore the group. After 30 days, the group and its associated contents are permanently deleted and cannot be restored.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/create-groups/restore-deleted-group
NEW QUESTION # 120
......
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
MS-102 Certification All-in-One Exam Guide Dec-2025: https://www.torrentexam.com/MS-102-exam-latest-torrent.html
Easily To Pass New MS-102 Premium Exam: https://drive.google.com/open?id=15xzj6ChJInEq9LbJhocgIbYf_z2ux9aj
